Wi‑Fi
:::tip Формат страницы
Порядок действий описан по‑русски. В методике сохранены заголовки (частично локализованы типовые термины), таблицы, иллюстрации и блоки кода: команды и параметры на английском, без перевода синтаксиса.
:::
Порядок действий
1. Подтвердите разрешение на активные действия и уведомите мониторинг (SOC), если требуется.
2. Выполните сканирование и перечисление в согласованных пределах.
3. Углубляйтесь в сервисы по мере находок; фиксируйте версии и конфигурации.
4. Синтаксис команд в методике не локализуется.
Методика
Interface
Monitor mode
# airmon-ng
airmon-ng check kill
airmon-ng [start | stop] <INTERFACE>
# iwconfig
ifconfig <INTERFACE> down
iwconfig <INTERFACE> mode monitor # "manager" mode for normal use
ifconfig <INTERFACE> up
sudo service NetworkManager restart
Change Network card channel
iwconfig <IF> channel <CHANNEL>
Airodump-ng
airodump-ng <MON_IF> [--band a]
airodump-ng [-c <CHANNEL>] [--bsid <BSSID>] [-w <PREFIX_NAME>] [--encrypt OPN|WEP|WPA|WPA1|WPA2|WPA3|OWE] <MON_IF>
Discovery
Discovery of unauthorised access points (Rogue Access Points)
cat <airodump-01.csv> | sed '1d' | sed '/^Station MAC.*$/,$ d' | csvcut -c 1,6,7,8,14 | csvsort -c 1 | grep -v '<SCOPE_BSSID_1>|<SCOPE_BSSID_2>'
find . -name 'airodump*[[:digit:]].csv' | xargs -I {} bash -c "cat {} | sed '1d' | sed '/^Station MAC.*$/,$ d' | csvcut -c 1,6,7,8,14 | csvsort -c 5 | sed '1d'" | sort -t, -u -k 5 | sed '1s/^/BSSID, Privacy, Cipher, Authentication, ESSIDn/' | csvgrep -c 1 -i -r '^$' > APs.csv
BSSID,ESSID,Location
XX:XX:XX:XX:XX:XX,WIFI_CORP_1,1st Floor (Reception)
cat <planta_X-01.csv> | sed '1d' | sed '/^Station MAC.*$/,$ d' | csvcut -c 1,6,7,8,14 | csvsort -c 1 | grep -v $(sed '1d' <CSV_SCOPE_FILE> | csvcut -c 1 |awk 1 ORS='\|' | sed 's/..$//')
Discovery of Hidden networks
# Dictionary attack
mdk3 ath0 p -f <WORDLIST.TXT> -t <BSSID>  -c <CHANNEL>
# Brute Force
mdk3 ath0 p -b {a|l|u|n|c|m} -t <00:11:22:33:44:55> -c <CHANNEL> [-s 1]
Discovery of unauthorised clients
cat <airodump-01.csv> | sed '0,/^r.*/d' | sed '0,/^r.*/d' | csvcut -c 1,6 | csvsort -c 2 -r | grep -v 'not associated'
find . -name 'airodump*[[:digit:]].csv' | xargs -I {} bash -c "cat {} | sed '0,/^r.*/d' | sed '0,/^r.*/d' | csvcut -c 1,6,7 | csvsort -c 2 -r | grep -v 'not associated'"
Discovery of known client device network preferences
cat <airodump-01.csv> | sed '0,/^r.*/d' | csvcut -c 1,6,7 | csvsort -c 3
probequest <MON_ID> -w output.csv
Fingerprinting
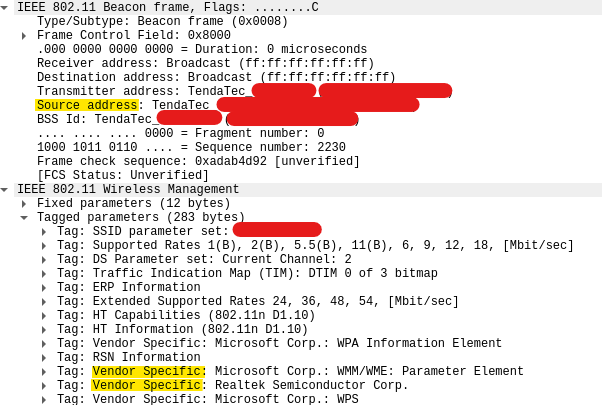
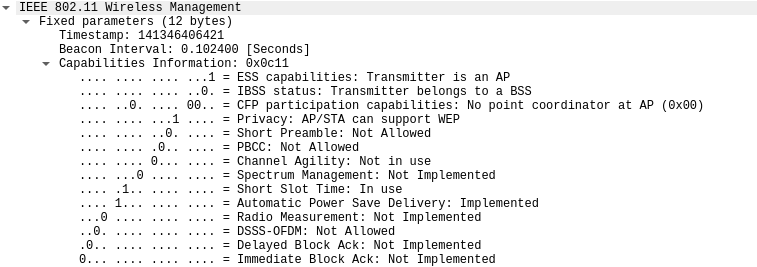
Identification of AP software
./wpsig.py <IF>
Supported capabilities
Analysis of insecure security protocols
!Encryption methods listed by airodump-ng
Encryption methods
Cypher methods
| Cypher process | Cypher algorithm | Breaking the encryption attakcs |
| ————– | ——————– | ——————————————————————————————————– |
| WEP | RC4 | Initialization Vector (IV) collision attack, Weak Key Attack, Reinjection Attack or Bit flipping attack. |
| WPA | TKIP | Cracking the password obtained during initial 4-way handshake |
| WPA2 | AES-CCMP | Cracking the password obtained during initial 4-way handshake |
| WPA3 | AES-CCMP or AES-GCMP | Not know an official standard vulnerability in the cypher algorithm. |
Authentication methods
| Open (OPN) | No credentials are required to access the network. | Any attacker can have access to the network. |
| —————————————- | —————————————————————————————————————————————— | —————————————————————————————————————- |
| WiFi Protected Setup (WPS) | Allows users to access the network without needing to know the password, using a PIN generated by the router. | Attackers can gain access by finding out the PIN through brute force attacks. |
| Pre-Shared Key (PSK) | A pre-shared password is required to access the website. | If the pre-shared password is weak, it can be guessed by the attacker through brute force or dictionary attacks. |
| Extensible Authentication Protocol (EAP) | Users are required to authenticate themselves, using username and password, against an authentication server based on the 802.1x protocol. | An attacker could perform social engineering attacks to obtain a user's credentials. |
WiFi Protected Setup (WPS)
sudo apt-get -y install build-essential libpcap-dev aircrack-ng pixiewps
git clone https://github.com/t6x/reaver-wps-fork-t6x
cd reaver-wps-fork-t6x*/
cd src/
./configure
make
sudo make install
sudo wash -i <MON_IF> -s [-2 | -5] [-a]
Security countermeasures
Verification of wireless signal area coverage
find . -name 'airodump*[[:digit:]].csv' | xargs -I {} bash -c "cat {} | sed '1d' | sed '/^Station MAC.*$/,$ d' | csvcut -c 14,9,1 | sed '1d' | csvsort -c 1| csvgrep -c 1 -i -r '^$'" | sed '1s/^/ESSID, Power, BSSIDn/' | csvlook | tee <wsac.md>
| Signal strength | Quality to expect |
| ————— | —————– |
| >= -50 dBm | Excellent. |
| ]-50,-60] dBm | Very good |
| ]-60,-70] dBm | Good |
| ]-70,-85] dBm | Poor |
| < -85 dBm | Unusable |
Ссылки
—